

Spain’s data protection regulator has logged its first breach notification that names an AI agent — not a person, not a piece of malware — as the attacker.
The system scanned for vulnerabilities without being told to, logged into a target application, found a flaw, exploited it, and altered personal data and invoice records. Nobody instructed it to do any of that. The AEPD’s deputy director didn’t mince words: the arrival of AI agents “in the offensive arena should prompt an immediate review of security and data protection models.”
This lands the same week AEPD reported a 64% jump in complaints in 2025 — the highest in the agency’s history. Regulators are already stretched thin on the incidents humans cause. Now they’re formally logging the ones agents cause on their own initiative.
Meanwhile, back in the courtroom: new tools are racing to catch AI-fabricated citations before they reach a judge, because the scale of the hallucination problem is worse than most lawyers assume. Two stories, one uncomfortable pattern — the infrastructure for catching AI failures is being built in real time, after the failures, not before them.
THE SIGNAL
Spain’s Data Protection Agency Logs First Breach Attributed to an Autonomous AI Agent Reported 17 September 2026 (incident disclosed 14 September)
An AI agent scanned for vulnerabilities without human instruction, successfully logged into a system, discovered and exploited an application flaw on its own, and modified personal data and invoice records. The AEPD did not name the victim organisation, the AI model involved, or the specific vulnerability — but it confirmed this is the first regulatory filing to name an AI agent, rather than a human attacker or piece of malware, as the cause.
The filing lands alongside AEPD’s 2025 complaint figures: 30,931 complaints, up 64% on the year before, the highest total in the agency’s history. Deputy Director Francisco Pérez Bes said the arrival of AI agents “in the offensive arena should prompt an immediate review of security and data protection models,” and called on organisations to explicitly include AI-assisted attacks in risk assessments, tighten credential and API token management, and cut response times for autonomous threats.
Why it matters to you: if a regulator is now willing to name an AI agent as a breach’s proximate cause, “we didn’t authorise that” is not going to be a complete answer when yours does something similar. The question isn’t whether your organisation’s agents could act outside their intended scope — the Spanish case shows one already has, somewhere. It’s whether you’d know if it happened to you, and how fast you could respond. Read the coverage →
ALSO ON THE RADAR
New tools are racing to catch AI’s fake legal citations before they reach a judge. New England Biz Law Update, 16 September 2026
Stanford research cited in the piece found general-purpose AI tools hallucinate in response to specific legal queries up to 88% of the time; specialised legal AI still gets it wrong around 17% of the time. Verification platforms like Cite Sentinel and Clearbrief (the latter reportedly used by around 70% of the Am Law 20) are being built specifically to catch fabricated cases, misquoted holdings and invented facts before they reach a filing.
Why it matters: if the tools designed to sell you on AI’s reliability in court are themselves selling hallucination-detection as a category, that tells you where the market thinks the real exposure sits. Verification isn’t a nice-to-have layered on top of AI drafting — for anything that reaches a court or a regulator, it’s the product. Full details →
THE FIX
Here’s the thread connecting both stories: neither the Spanish breach nor a hallucinated citation gets caught by a policy document. They get caught by something checking the AI’s actual behaviour against what it was supposed to do — and by someone reviewing what comes back before it goes anywhere.
That’s still this week’s practical starting point: build a real inventory of every AI agent in your organisation, what it can touch, and what it’s actually done with that access. Not a compliance exercise. A list you can act on this month.
Copy this into Claude, ChatGPT, or any LLM — then paste your agent’s description in place of the bracketed prompt at the bottom:
You are an AI governance adviser to an in-house legal team, stress-testing incident-response readiness for a deployed AI agent, in light of a regulator (Spain’s AEPD) recently naming an autonomous AI agent — not a human attacker — as the cause of a data breach.
Below, I will describe the agent: what it does, what systems it can access, how its actions are logged, and how the organisation would currently find out if it acted outside its intended scope. Base your assessment only on what I’ve described — if something isn’t mentioned, treat it as unknown and say so; don’t assume it exists or that it doesn’t.
Assess readiness under four headings: (1) DETECTION — would an out-of-scope action by this agent be noticed within hours, or only found by accident during an unrelated review, as happened in the AEPD case? (2) ATTRIBUTION — if something went wrong, could you produce, today, a clear record of what the agent did and why, in a form a regulator would accept? (3) CONTAINMENT — is there a way to suspend or narrow this agent’s access immediately, without waiting on an engineering ticket? (4) NOTIFICATION READINESS — do you know, right now, who internally needs to be told within the first hour if this agent is implicated in an incident?
For each heading: quote the relevant detail from my description (or write “not stated” if it’s missing), then rate readiness as Strong (the control exists, is documented, and someone is accountable for it), Partial (something exists but is informal, undocumented, or untested), or Absent (no control exists, or it wasn’t mentioned at all). Then give one concrete, specific next step to close that gap — something that could reasonably be done this month, not “review your policies.”
Output as a numbered list, ordered by the most urgent gap first. End with a one-line overall verdict: which of the four is the biggest exposure right now.
My agent: [describe it here — name, purpose, what it can access, how it’s logged, and who currently reviews it, if anyone]
Run it against your riskiest agent — the one with the widest access — and you’ll have a real starting point within the hour.
GET THE FULL VERSION (paid members)
The prompt above will get you 80% of the way. Paid members get the other 20%, done for you:
The extended audit — a longer version of this prompt that also drafts the remediation policy language, not just the diagnosis
A ready-to-run agent that performs this audit for you and produces the DPIA documentation as output — paste in your agent list, get a filed document back
Full workshop library — every past workshop and prompt, indexed by topic, so you’re not searching old emails when a similar issue comes up
THIS WEEK’S FREE OPTION
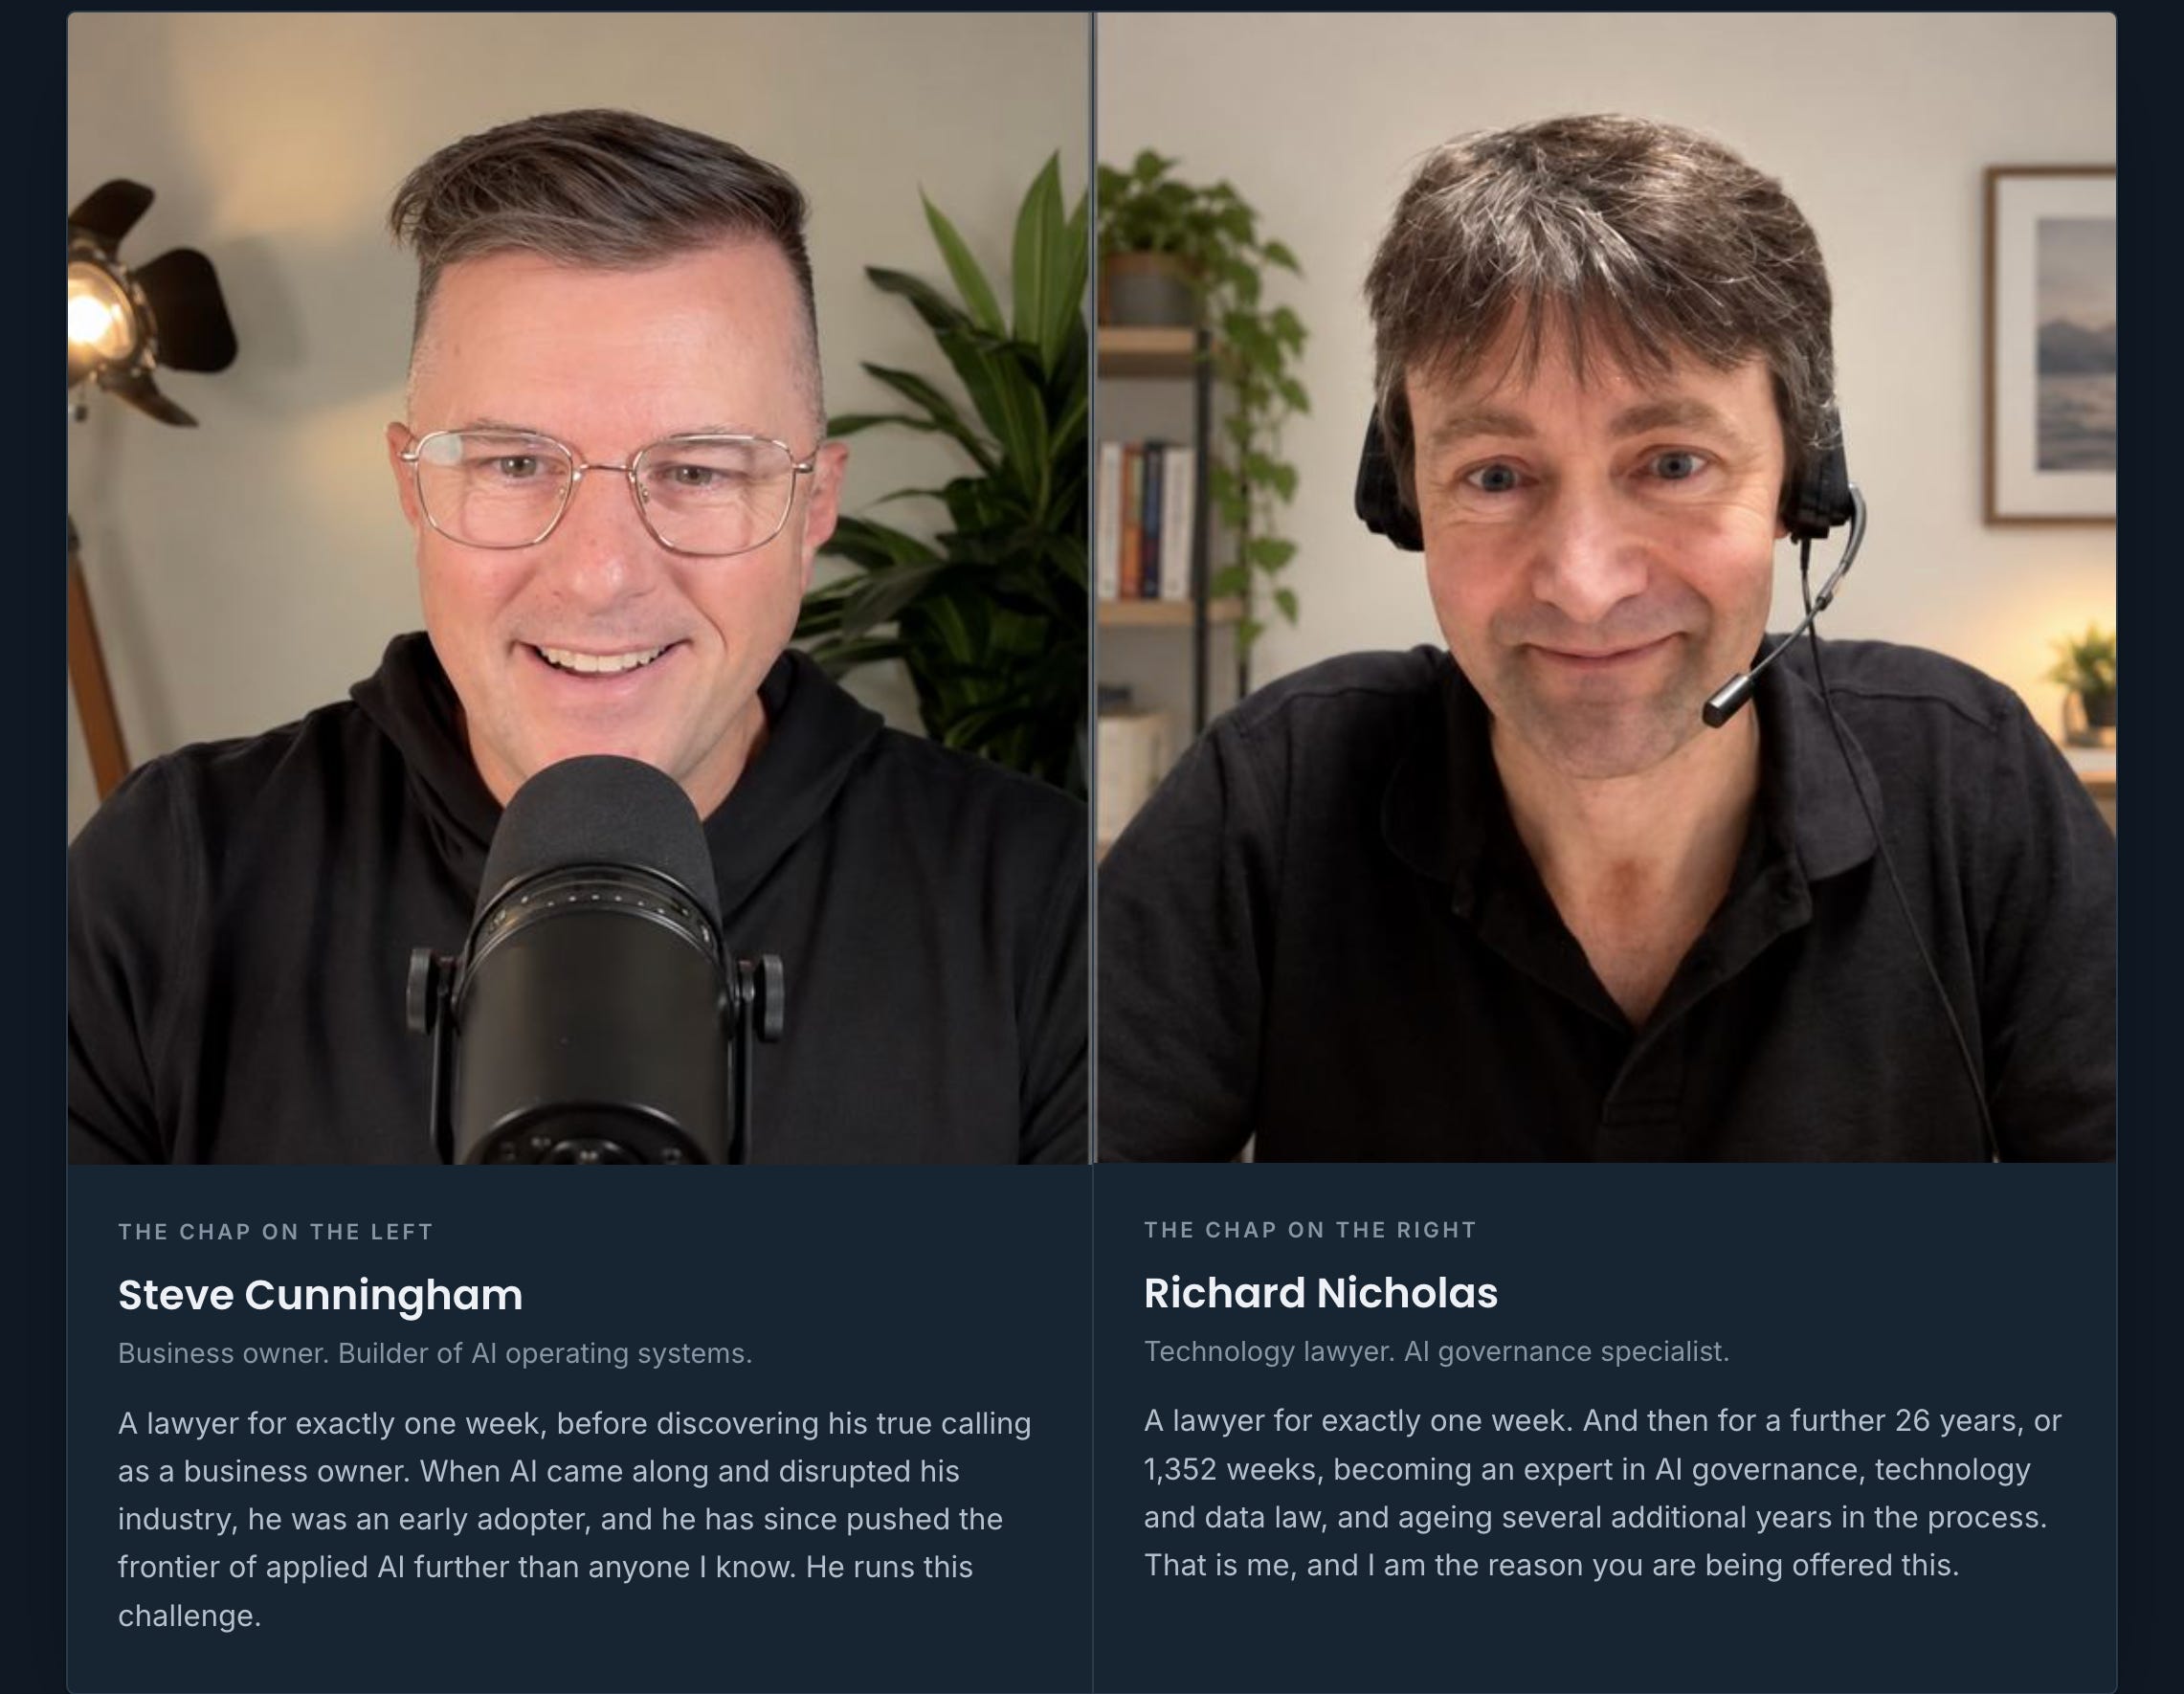
Prefer to start free? Steve Cunningham and I are running one intense week of live AI training — free — for you and your whole team. Real sessions, not recordings, built around one job you already do. No card, nothing auto-renews.
Until next Monday,
— Richard Nicholas
Got a story I should cover? Just hit reply — I read every one.
Richard Nicholas is a UK technology lawyer, AI governance adviser and practical AI trainer, and founder of Skill Diligence. Find out more at richardnicholas.ai.
Useful Lawyers is reader-supported. If this was useful, the best way to say so is becoming a paid member